Decade-Long Flaw in XRP Ledger Can Mint Tokens Out of Thin Air: RippleX Urgently Patches with No On-Chain Exploitation Detected
Author: Shaurya Malwa
Translated by: TechFlow
TechFlow Briefing: Researchers have demonstrated that a long-standing vulnerability in the XRP Ledger payment path could enable the creation of spendable XRP with minimal funding from the sender, undermining its "fixed supply" promise. RippleX urgently patched it on September 25 via xrpld 3.4.1, stating there is no evidence it was exploited on public networks; for institutions and holders relying on the supply cap, this served as an on-chain monetary integrity stress test.
According to a security report released on Friday, a flaw in the XRP Ledger payment system could have enabled attackers to generate large quantities of new XRP at virtually no cost, breaking the token's fixed supply rules.
The vulnerability is believed to date back to 2015, discovered by researcher Cayden Liao and Veria AI, and internally reported on September 22. Engineers from Ripple's development team, RippleX, reproduced the attack on an isolated server and confirmed the newly minted XRP could be spent in subsequent transactions.
RippleX stated that there is no evidence the flaw has been exploited on any public network.
All 100 billion XRP were generated when the ledger went live in 2012, and its software was designed to prevent any future issuance. However, this security flaw could have allowed attackers to conjure XRP out of thin air and sell it on exchanges, weakening the supply cap upon which institutions rely when using the network.
The attack vector exploits the ledger's built-in exchange: accounts post offers there to swap one token for another.
Theoretically, an attacker could open hundreds of accounts, each using a tiny amount of tokens to claim an exceptionally large quantity of XRP, then initiate a single payment to sweep all those offers at once.
The total XRP to be paid would become so large that the software fails to count correctly, allowing the attacker's sell-order accounts to receive full payment while their buy-order accounts go almost entirely undeducted—granting the attacker XRP that previously did not exist.
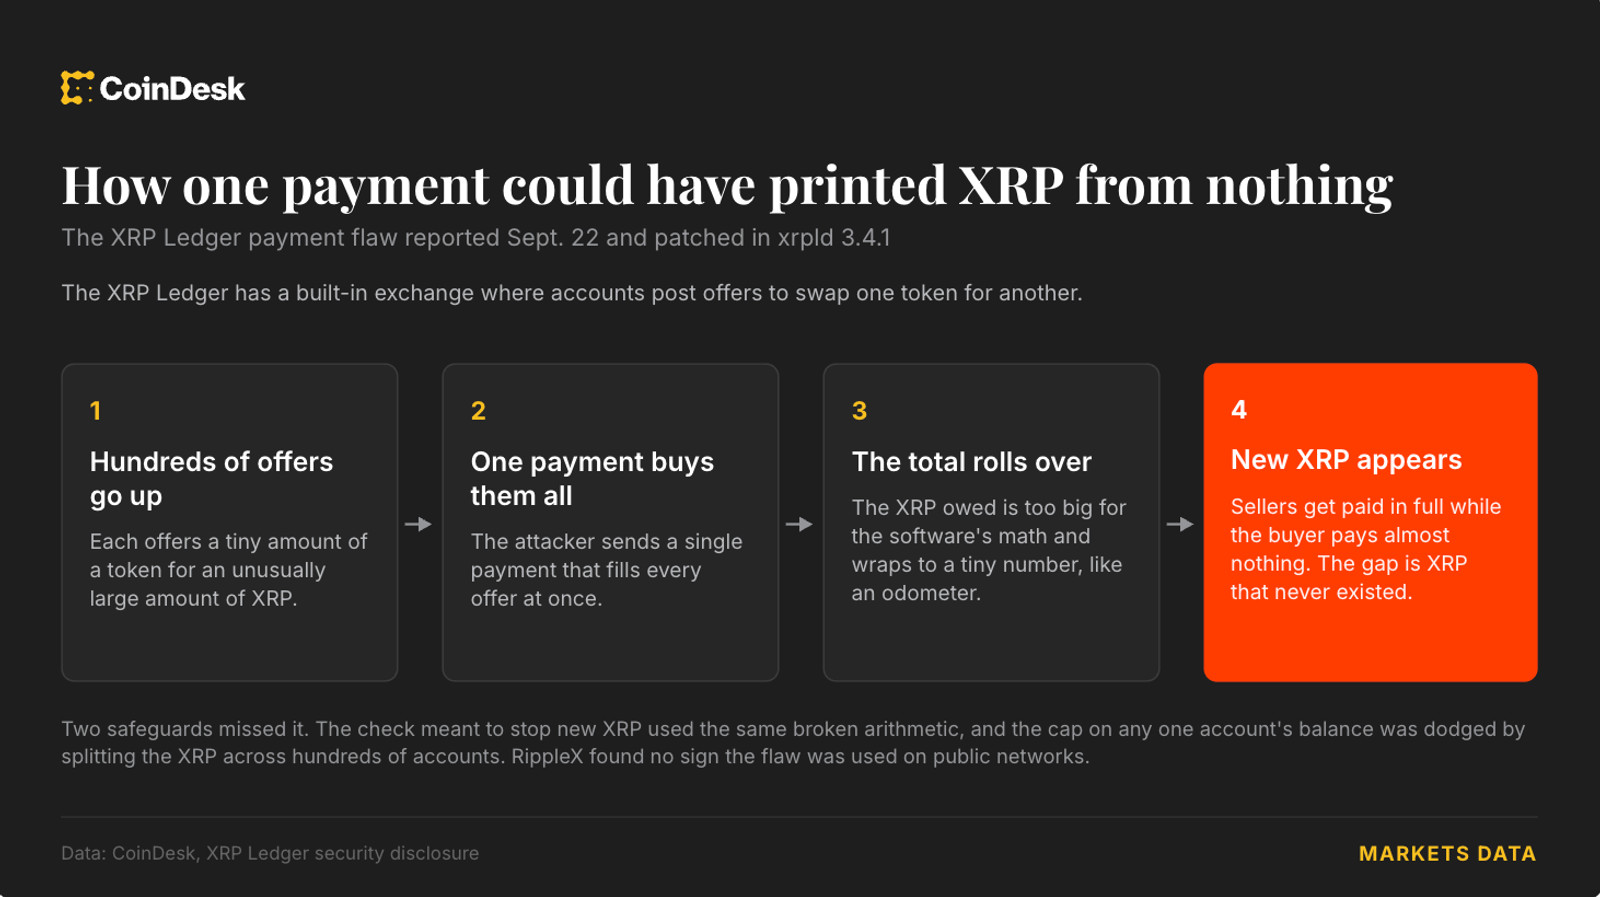
The XRP Ledger runs a check after every transaction to verify that no new XRP has appeared, but that check relies on the miscalculated total, causing it to miss the breach. Another limit on how much XRP a single account can receive would also fail to trigger, as the attack disperses XRP across hundreds of accounts.
The researchers' method requires only a few hundred XRP to open these accounts, most of which can be reclaimed, plus transaction fees.
Developers delivered the patch in ledger server software xrpld 3.4.1 on September 25, without initially disclosing what had been fixed.
Since July, a string of long-hidden crypto security vulnerabilities have been uncovered with AI assistance, adding this incident to the roster, including the Coldcard wallet flaw that led to the theft of at least 1,367 BTC, and those that forced Core Lightning to require Bitcoin node operators to disconnect.
Join TechFlow official community to stay tuned
Telegram:https://t.me/TechFlowDaily
X (Twitter):https://x.com/TechFlowPost
X (Twitter) EN:https://x.com/BlockFlow_News
 CoinDesk